Guides
Lovable Apps Data Exposure: Check Your Supabase RLS
Researchers found thousands of Lovable apps on Supabase exposing user data without a login. Here's how to check your app, fix open rules, and when to get help.
Researchers found thousands of Lovable apps on Supabase exposing user data without a login. Here's how to check your app, fix open rules, and when to get help.
ChatGPT Wallet lets OpenAI's dots agents pay with a tokenized card after a Face ID check. What launched, the fine print, and what you should do now.
Apache 2.4.71 fixes CVE-2026-119618, a critical HTTP/2 RCE in 2.4.55 to 2.4.70 first found by Anthropic's AI scanner. Here's how to check, patch or turn off h2.
Fireworks AI says an October breach exposed billing data, secrets, datasets and partial model weights, and Notion AI chats were hit. What to rotate now.
Claude Code's "Don't ask again" can save passwords and API keys in settings.local.json. Apiiro found 1,122 public GitHub copies with secrets. Here's what to do.
A critical OpenSSH bug dubbed SSHole lets attackers log into passwordless Alpine accounts. Version 10.6p2 patches it, and attacks started within hours.
OpenAI launched GPT-6 Cyber, a Critical cybersecurity model for Daybreak Red. Benchmarks, scope alignment, Linux/Firefox claims, and what U.S. teams should do.
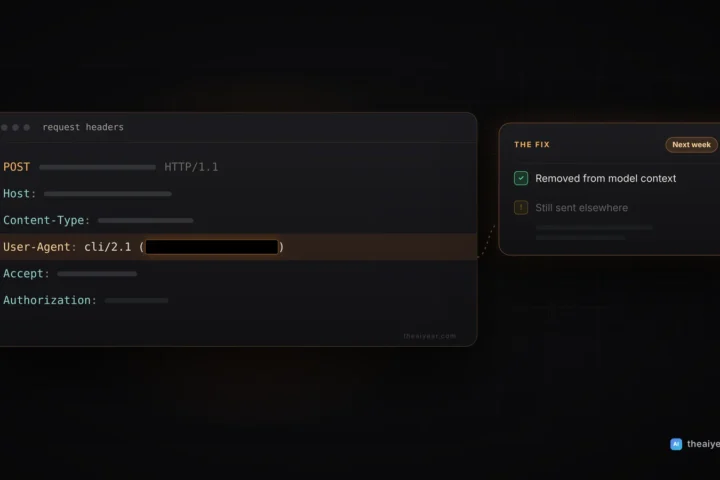
Claude Code put users' account emails in web request headers. Here's what Anthropic's 2.1.317 fix covers, what it misses, and what to check today.
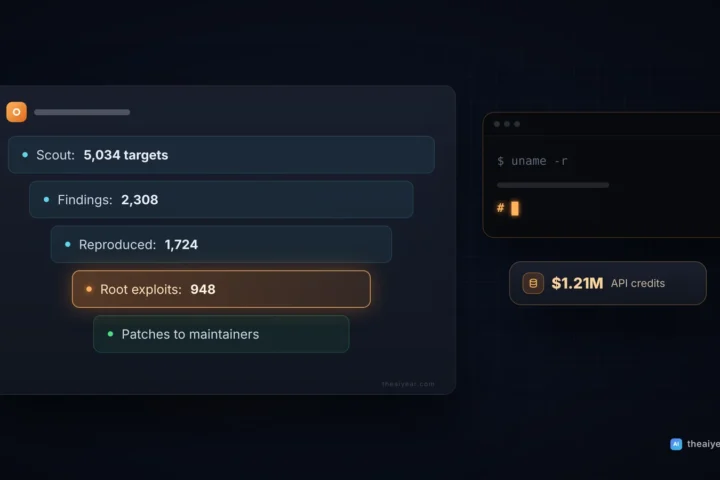
OpenAI's AI pipeline found 948 Linux kernel root exploits for $1.2M. What it really means, what's patched, and what Linux admins should do this week.
Postman desktop quietly added plugins to Claude Code and Codex and pre-approved its own startup hook. What happened, what it means, and what to check.
One email when a new guide or story goes live. No spam, unsubscribe anytime.
By subscribing you agree to our privacy policy.